
One verification interface for every output One API. Separate evidence.
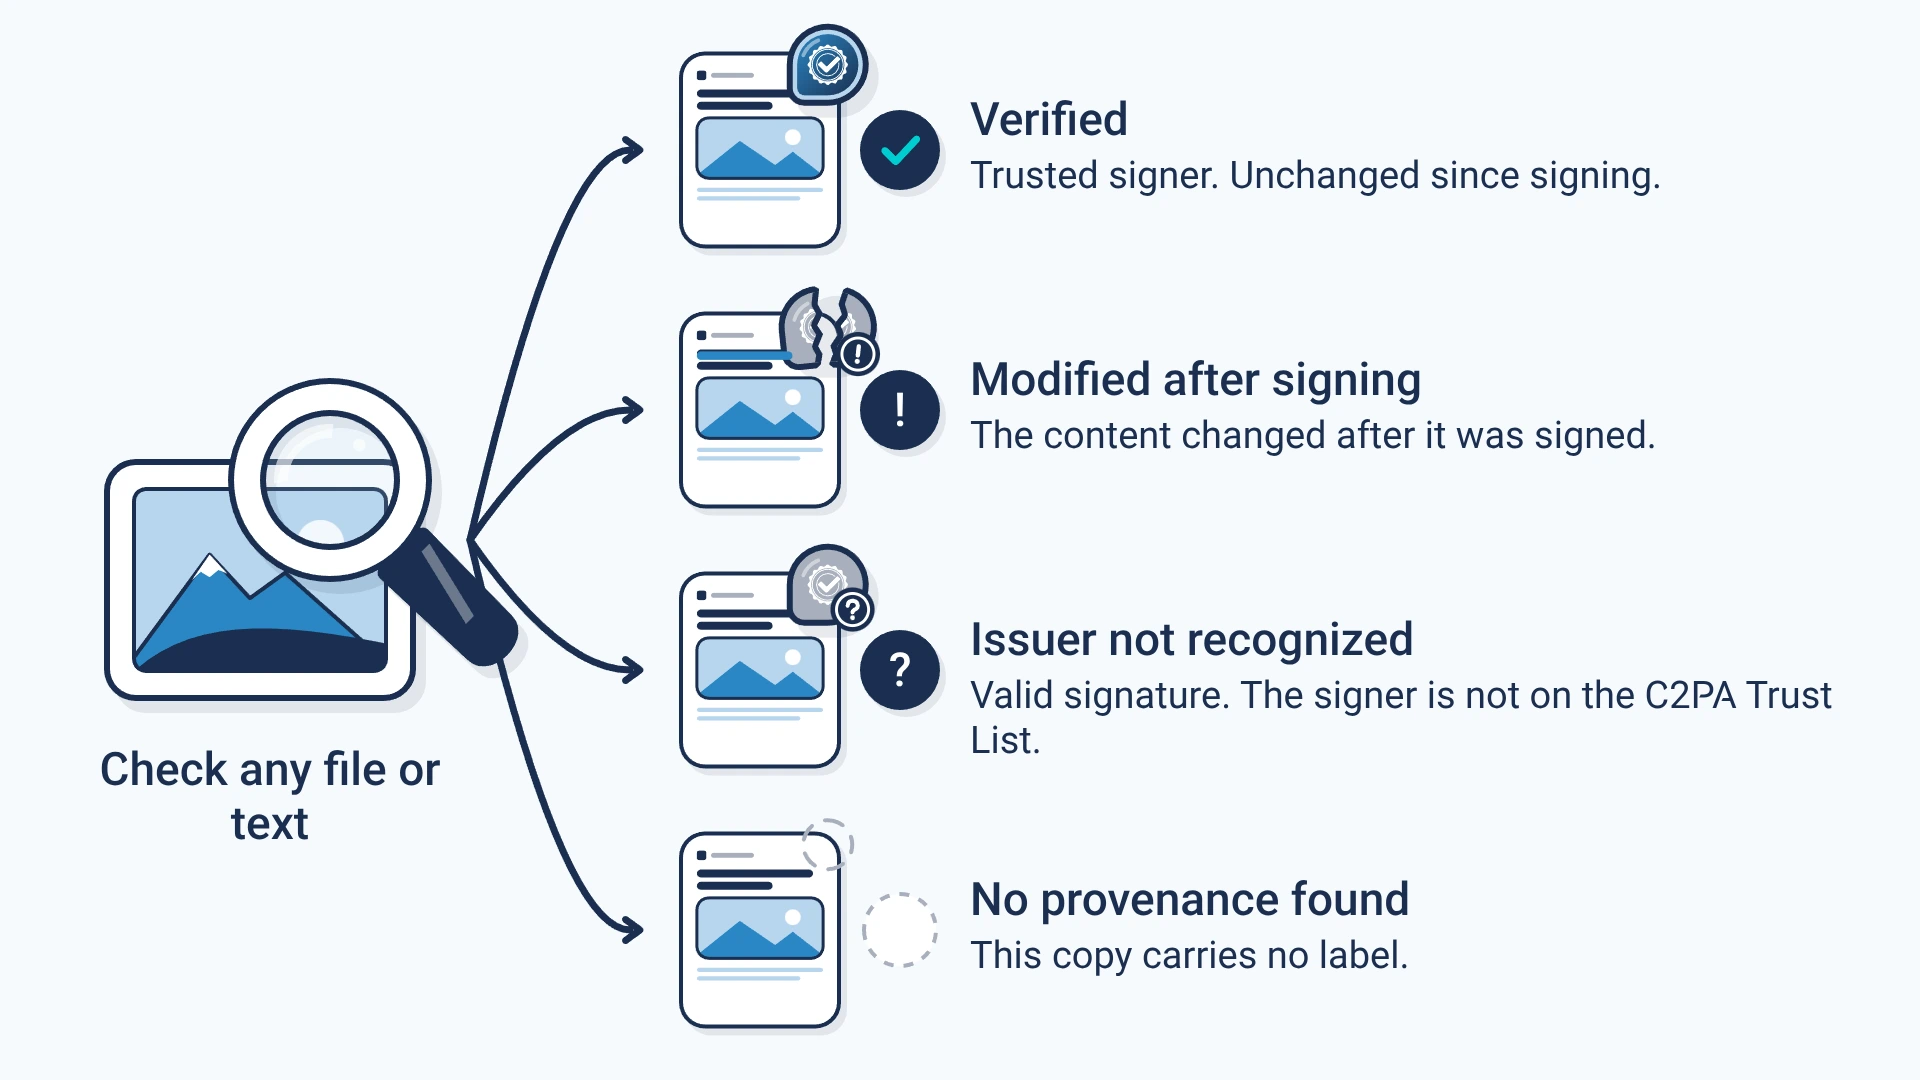
Encypher Verify reads the C2PAC2PA: The Coalition for Content Provenance and Authenticity: the group that publishes the open standard for content labels. label and any supported watermark in text, images, audio, video and documents such as PDF and Word. Each check gives its own result. Your team decides what to trust.
One vendor. One integration. Every output type. The basic check is free, with no account and no API keyAPI key: A secret string that identifies your account when your software calls an API. Keep it out of public code..
- One API
- Send text or a file through its matching APIAPI: Application programming interface: a way for one program to ask another to do a job, such as sign a file. endpoint. Each runs the checks that fit the content type.
- Separate evidence
- The signature, the watermark, a found record and your policy each get a result. Nothing hides in one score.
- Any signer
- It reads C2PA labels from any signer, not just ours.
- Free to try
- The public check needs no account. Try it now
Five checks, one answer
Read the content type
Pick the checks that fit: label, watermark and policy.
Check the label
Check the C2PA manifestC2PA manifest: The signed label itself: a small package inside a file that records who signed it, what they declared and how to check it.: who signed it, when, and its hard bindingHard binding: A hash of the content's signed bytes stored in the label, so a change to those bytes makes the check fail..
Look for watermarks
Run the supported watermarkWatermark: A mark placed in the content itself, visible or hidden, so it can be found again after the file is copied. checks for text, images, audio or video.
Recover a stripped record
Follow a soft binding back to the record when one applies.
Return the evidence
One reply keeps each signal, limit and policy reason apart.
What each result tells you
| Possible results | What it tells you | |
|---|---|---|
| C2PA credential | Valid, invalid or absent | Who signed, and whether the content changed |
| Watermark signal | Detected, not detected or unsupported | Evidence from that provider's method |
| Soft-binding recovery | Found, not found or does not apply | Whether a linked record was found |
| Policy result | Meets, incomplete or fails policy | A decision with named reasons |
When the label was stripped
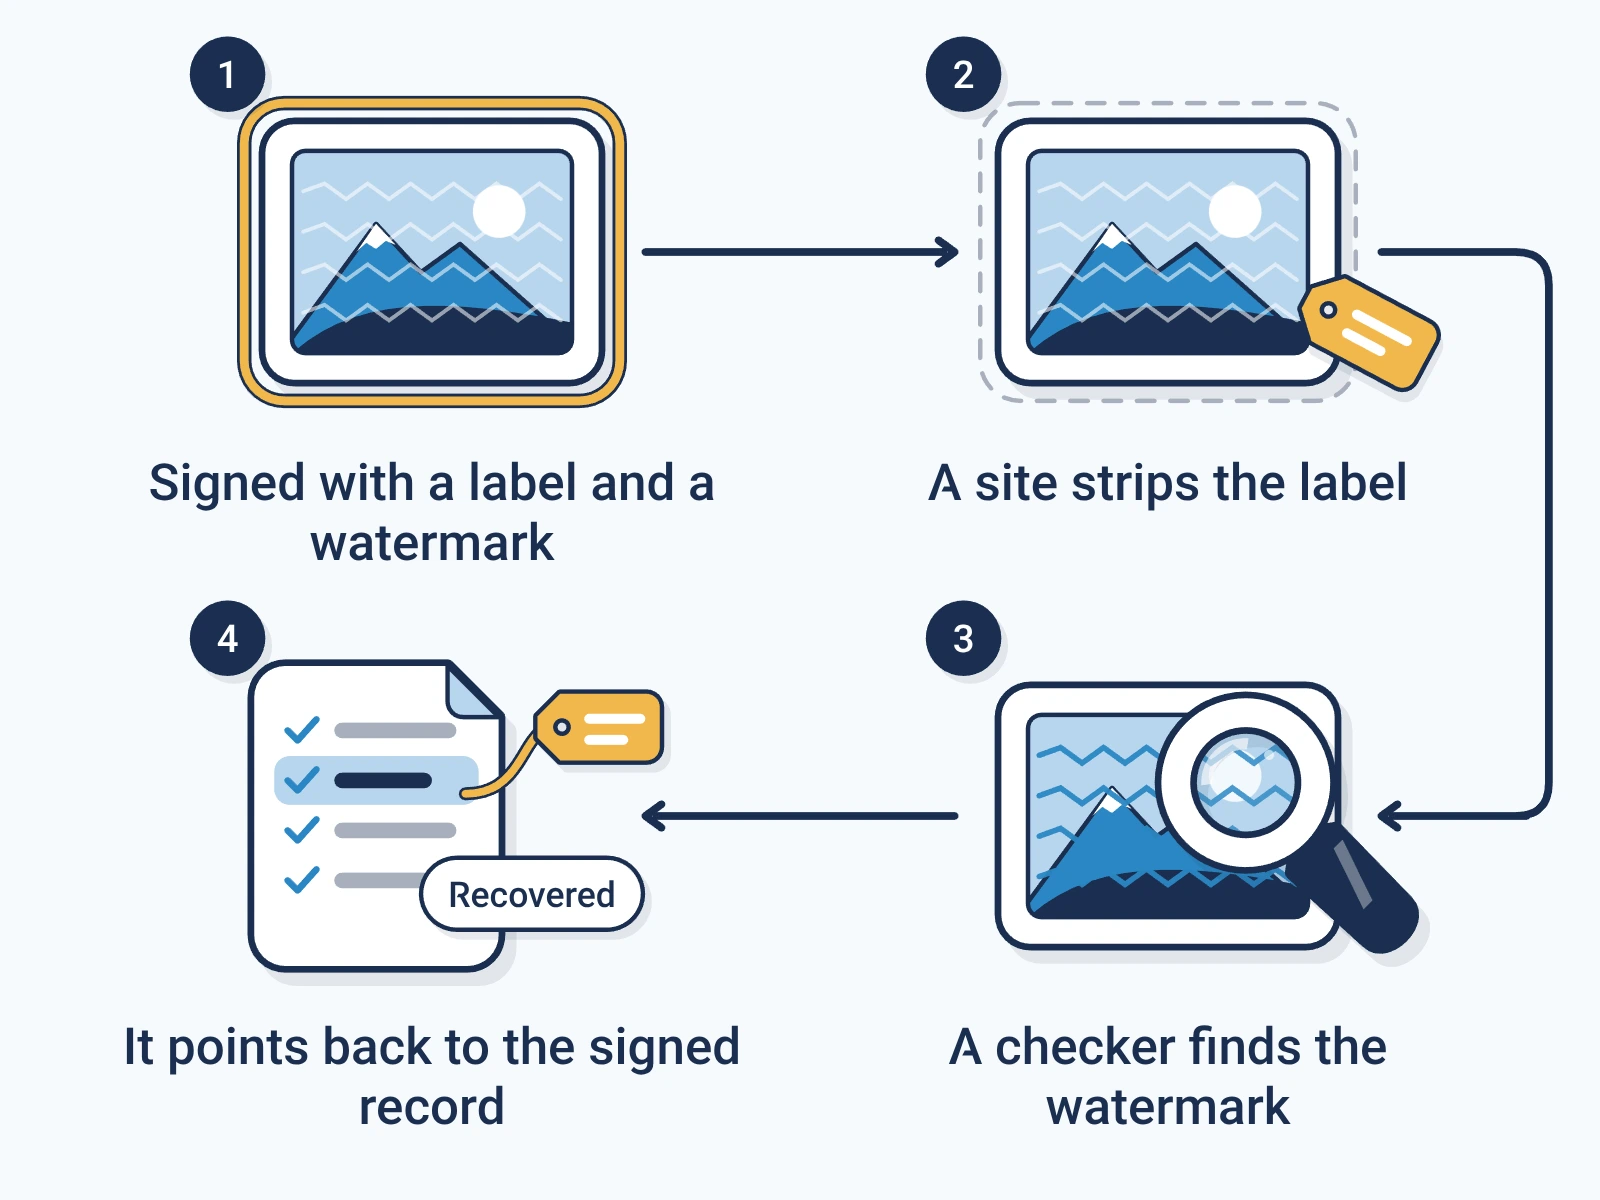
Platforms often remove metadataMetadata: Data stored beside the content in a file, such as author, camera or date. Many tools strip it when they copy or upload a file. on upload. A soft bindingSoft binding: A watermark or fingerprint that can find a content label again after the file was copied or its metadata stripped. can still lead back to the signed record: a watermark in the content points to where the record lives.
Recovery works when the applicable watermark and resolverResolver: A lookup service that takes an ID found in a watermark or fingerprint and returns the matching provenance record. are present. The result says so plainly when they are not.
Who uses it
- Article 50 teams
- Mark output, check it and keep the evidence for the EU AI ActEU AI Act: The European Union's law on artificial intelligence, which includes rules for marking AI-made content., Article 50Article 50: The EU AI Act rule that AI-made content be marked in a form software can read, and deepfakes disclosed.. Encypher supplies technical infrastructure and evidence. Your team and counsel retain responsibility for legal scope, disclosure, and governance.
- Platforms
- Put one intake check in front of content from many tools. Accept, reject or review each file under your own policy.
For engineers
Show the technical detail
curl -X POST https://api.encypher.com/api/v1/public/verify \
  -H "Content-Type: application/json" \
  -d '{"text": "Paste signed text here."}'
curl -X POST https://api.encypher.com/api/v1/public/verify/media \
-F "file=@photo.jpg"# A file whose embedded record was removed:
# look up the linked record through its soft binding
POST /api/v1/public/verify/soft-binding- Hard binding
- A hash of the content inside the signed manifest. If one byte changes, the check fails.
- Recovery limits
- A generic watermark is not a C2PA soft binding. Recovery needs the identifier, a resolver, a reachable record and a supported path.
- Reference
- API reference and the verify API page.
Create. Mark. Endure.
Start with one output: mark it, check it, and keep the evidence.